In OCI's shared security model, who secures workloads deployed on OCI?
Select an option, then click Submit answer.
- ○ The customer secures their workloads
- ○ Oracle secures all customer data
- ○ Third-party auditors only
- ○ Nobody is responsible
Loading demo links...
Showing 1–12 of 12 questions
In OCI's shared security model, who secures workloads deployed on OCI?
Select an option, then click Submit answer.
Which principle grants users only the access they need?
Select an option, then click Submit answer.
What does defense in depth mean for OCI designs?
Select an option, then click Submit answer.
Which OCI feature enforces mandatory security controls in a compartment hierarchy?
Select an option, then click Submit answer.
What is the first step to securing an OCI tenancy?
Select an option, then click Submit answer.
Which two are customer responsibilities in OCI? (Choose two.)
Select all that apply, then click Submit answer.
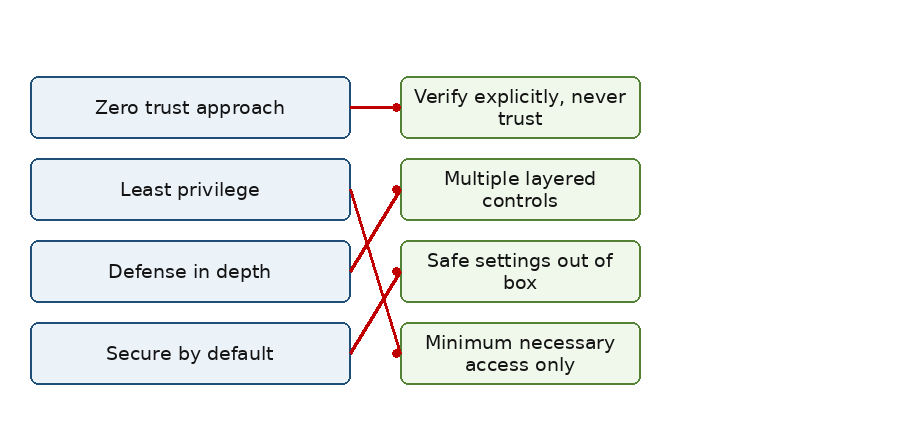
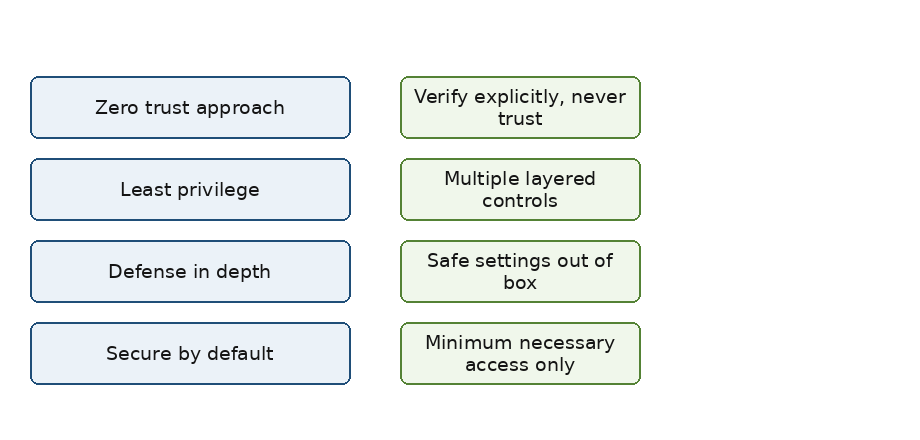
DRAG DROP
Match each security principle with its meaning.
Items to match: Least privilege, Defense in depth, Zero trust approach, Secure by default.

Answer is in the explanation below.
CORRECT TEXT
Layering multiple independent security controls is defense in ______.
Answer is in the explanation below.
What does an OCI IAM policy statement define?
Select an option, then click Submit answer.
Which two are IAM best practices? (Choose two.)
Select all that apply, then click Submit answer.
Which two can be policy subjects? (Choose two.)
Select all that apply, then click Submit answer.
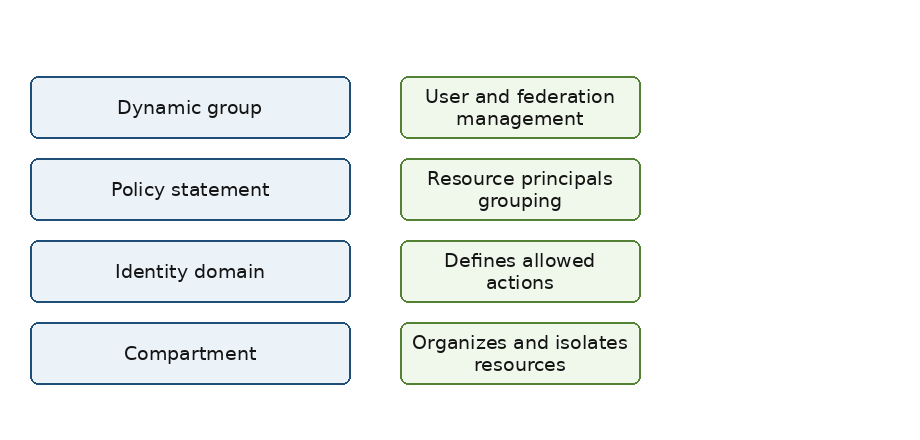
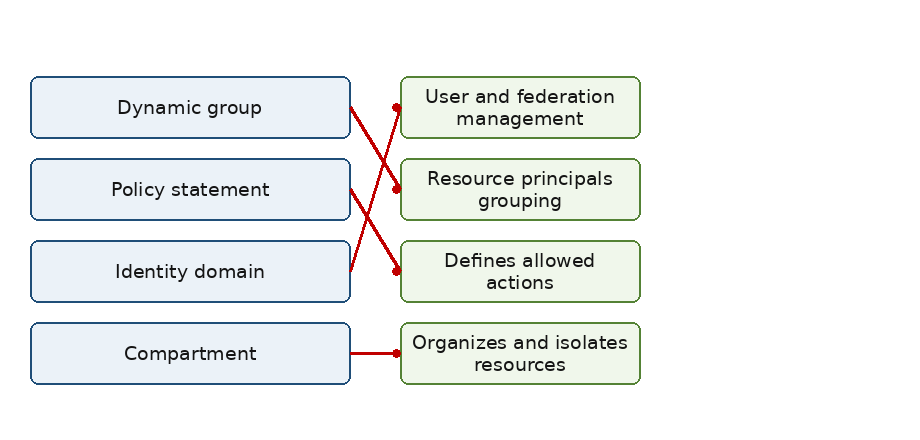
DRAG DROP
Match each IAM element with its role.
Items to match: Policy statement, Compartment, Dynamic group, Identity domain.

Answer is in the explanation below.