How is the ISA/IEC 62443 series of standards organized?
Select an option, then click Submit answer.
- ○ General, policies, system, component
- ○ General, network, cloud, mobile
- ○ Policies, people, products, patents
- ○ System, software, services, support
Loading demo links...
Showing 1–12 of 12 questions
How is the ISA/IEC 62443 series of standards organized?
Select an option, then click Submit answer.
What does a security level in ISA/IEC 62443 describe?
Select an option, then click Submit answer.
CORRECT TEXT
ISA/IEC 62443-3-3 defines system security requirements and ______ levels for IACS systems.
Answer is in the explanation below.
Which part of the series covers terminology, concepts, and models?
Select an option, then click Submit answer.
Which concepts are foundational models in ISA/IEC 62443? (Choose two.)
Select all that apply, then click Submit answer.
What is a conduit in the zones and conduits model?
Select an option, then click Submit answer.
How many security levels does ISA/IEC 62443 define, including level zero?
Select an option, then click Submit answer.
DRAG DROP
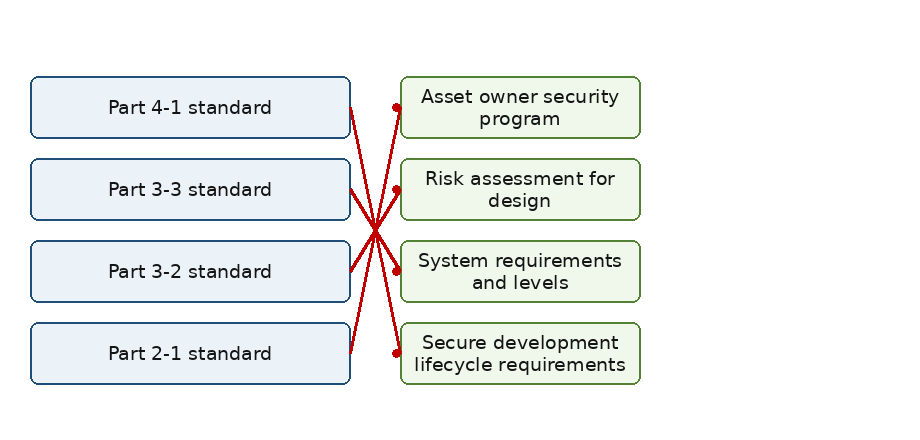
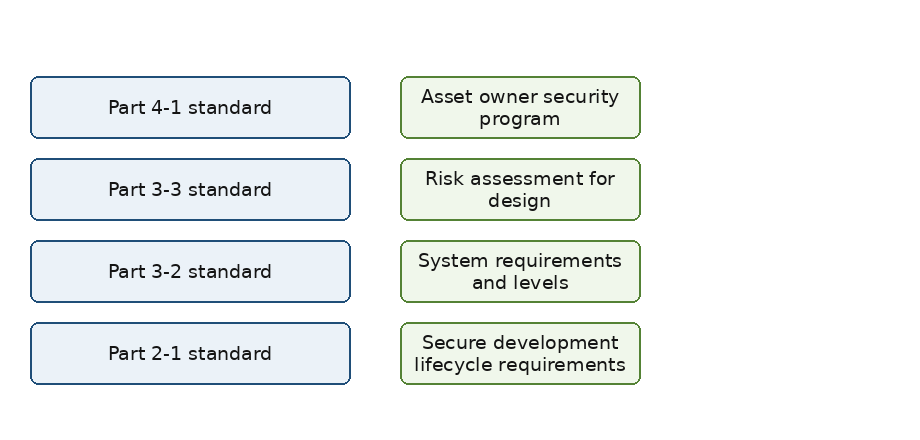
Match each 62443 part to its subject.
Items to match: Part 2-1 standard, Part 3-2 standard, Part 3-3 standard, Part 4-1 standard.

Answer is in the explanation below.
What distinguishes a target security level from an achieved security level?
Select an option, then click Submit answer.
Which statements about zones are correct? (Choose two.)
Select all that apply, then click Submit answer.
DRAG DROP
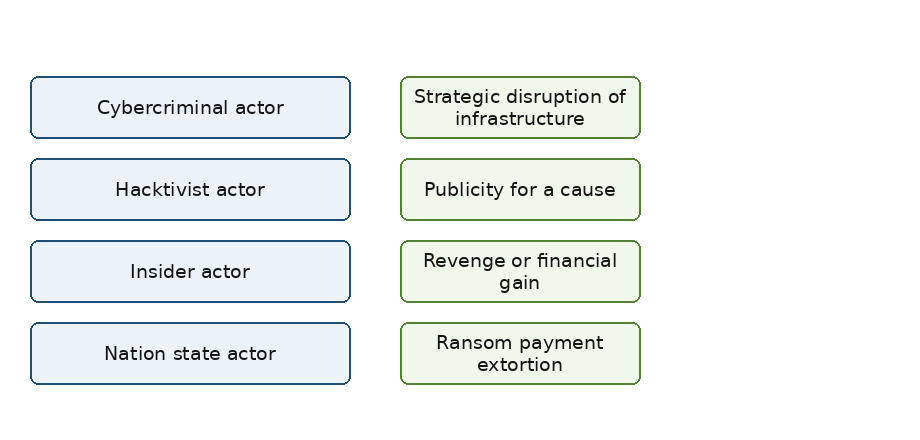
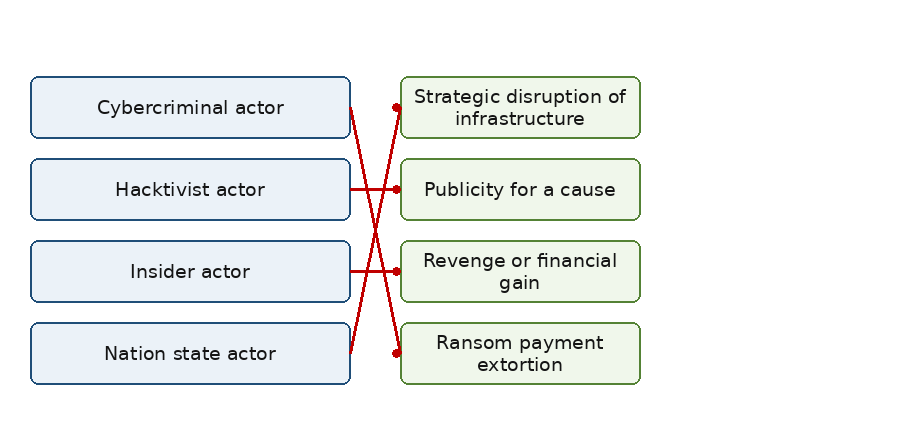
Match each threat actor to a typical motivation.
Items to match: Nation state actor, Hacktivist actor, Insider actor, Cybercriminal actor.

Answer is in the explanation below.
Which are common IACS threat sources? (Choose two.)
Select all that apply, then click Submit answer.