What does ISO/IEC 27032 primarily provide?
Select an option, then click Submit answer.
- ○ Guidelines for cybersecurity improvement
- ○ Requirements for ISMS certification
- ○ Rules for software licensing
- ○ Standards for hardware manufacture
Loading demo links...
Showing 1–12 of 12 questions
What does ISO/IEC 27032 primarily provide?
Select an option, then click Submit answer.
How is cyberspace best described?
Select an option, then click Submit answer.
Which domains does cybersecurity depend on?
Select an option, then click Submit answer.
What does CIIP stand for in 27032?
Select an option, then click Submit answer.
Why do stakeholders matter in cybersecurity?
Select an option, then click Submit answer.
What is the Lead Manager role?
Select an option, then click Submit answer.
Which domains relate to cybersecurity? (Choose two.)
Select all that apply, then click Submit answer.
Which statements describe the programme correctly? (Choose two.)
Select all that apply, then click Submit answer.
Who should lead cybersecurity work? (Choose two.)
Select all that apply, then click Submit answer.
DRAG DROP
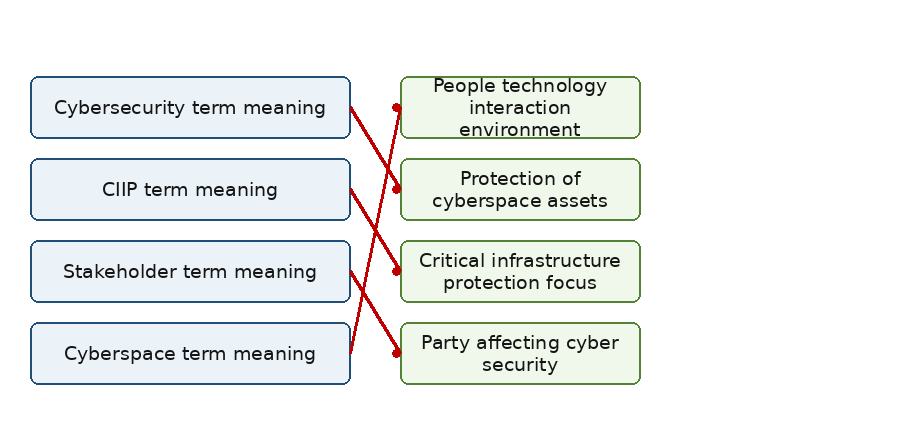
Match each term to its meaning.
Items to match: Cyberspace term meaning, Cybersecurity term meaning, CIIP term meaning, Stakeholder term meaning.

Answer is in the explanation below.
CORRECT TEXT
ISO/IEC ______ provides guidelines for cybersecurity and stakeholder collaboration.
Answer is in the explanation below.
DRAG DROP
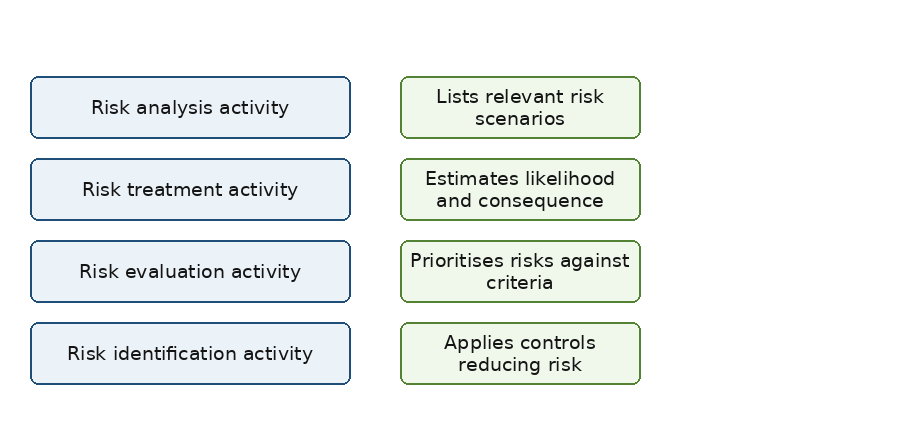
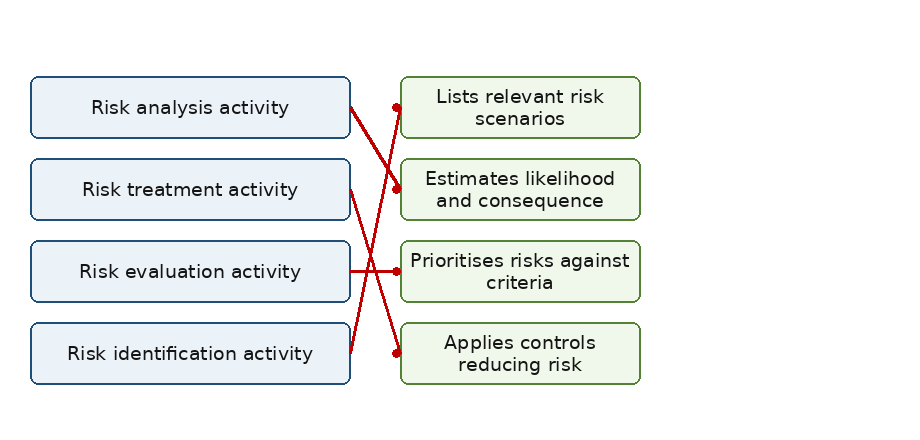
Match each risk activity to its output.
Items to match: Risk identification activity, Risk analysis activity, Risk evaluation activity, Risk treatment activity.

Answer is in the explanation below.