What is the core assumption of Zero Trust?
Select an option, then click Submit answer.
- ○ Never trust, always verify access
- ○ Trust internal network users
- ○ Verify once at perimeter only
- ○ Trust devices by default
Loading demo links...
Showing 1–12 of 12 questions
What is the core assumption of Zero Trust?
Select an option, then click Submit answer.
Which NIST publication defines Zero Trust Architecture?
Select an option, then click Submit answer.
Which of these is one of the seven NIST Zero Trust tenets?
Select an option, then click Submit answer.
What are the pillars in the CISA Zero Trust Maturity Model?
Select an option, then click Submit answer.
What does 'assume breach' change in design?
Select an option, then click Submit answer.
Which principle limits a compromised account's damage?
Select an option, then click Submit answer.
Which two are Zero Trust tenets/practices? (Choose two.)
Select all that apply, then click Submit answer.
Which two limit lateral movement? (Choose two.)
Select all that apply, then click Submit answer.
Which two are CISA maturity model pillars? (Choose two.)
Select all that apply, then click Submit answer.
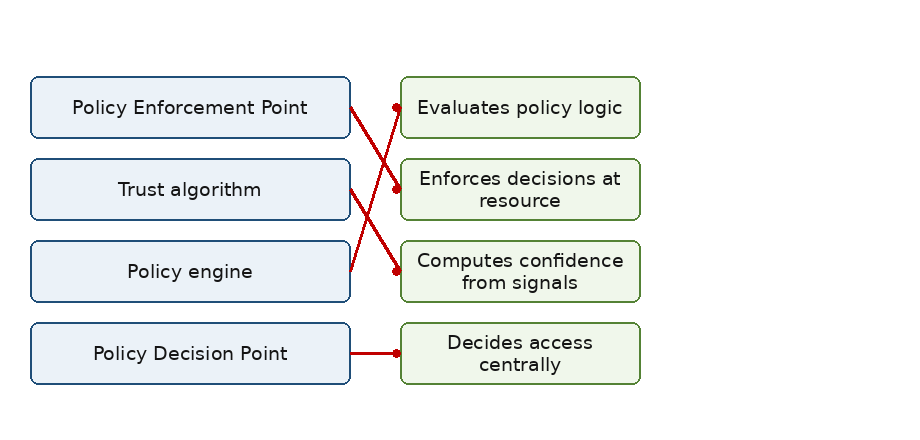
DRAG DROP
Match each ZTA component with its role.
Items to match: Policy Decision Point, Policy Enforcement Point, Policy engine, Trust algorithm.

Answer is in the explanation below.
CORRECT TEXT
Zero Trust's core mantra is 'never trust, always ______'.
Answer is in the explanation below.
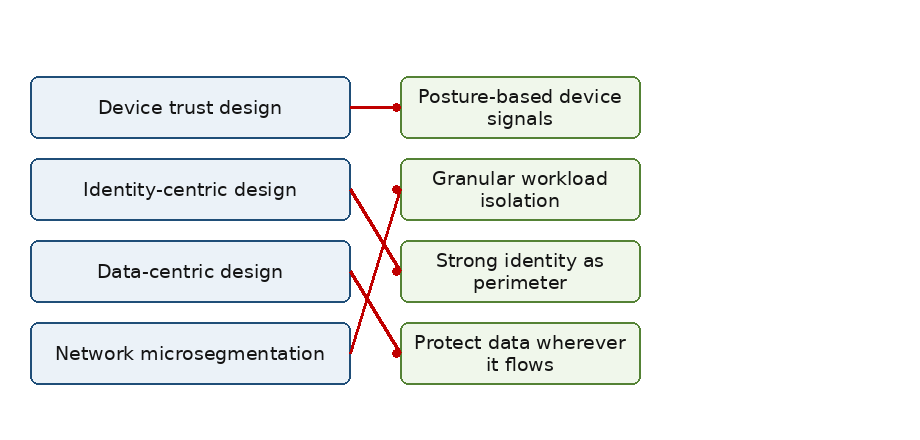
DRAG DROP
Match each design approach with its focus.
Items to match: Identity-centric design, Data-centric design, Network microsegmentation, Device trust design.

Answer is in the explanation below.