What does threat modeling during design primarily produce?
Select an option, then click Submit answer.
- ○ Threats and countermeasures per component
- ○ Working exploit code
- ○ Marketing feature lists
- ○ Deployment schedules
Loading demo links...
Showing 1–12 of 12 questions
What does threat modeling during design primarily produce?
Select an option, then click Submit answer.
In STRIDE, what does the 'T' stand for?
Select an option, then click Submit answer.
Which OWASP risk tops web application lists most years?
Select an option, then click Submit answer.
Security requirements gathering should trace controls to what?
Select an option, then click Submit answer.
What is an abuse case in requirements work?
Select an option, then click Submit answer.
Defense-in-depth for a Java web app means?
Select an option, then click Submit answer.
Which two are STRIDE categories? (Choose two.)
Select all that apply, then click Submit answer.
Which two belong in security requirements? (Choose two.)
Select all that apply, then click Submit answer.
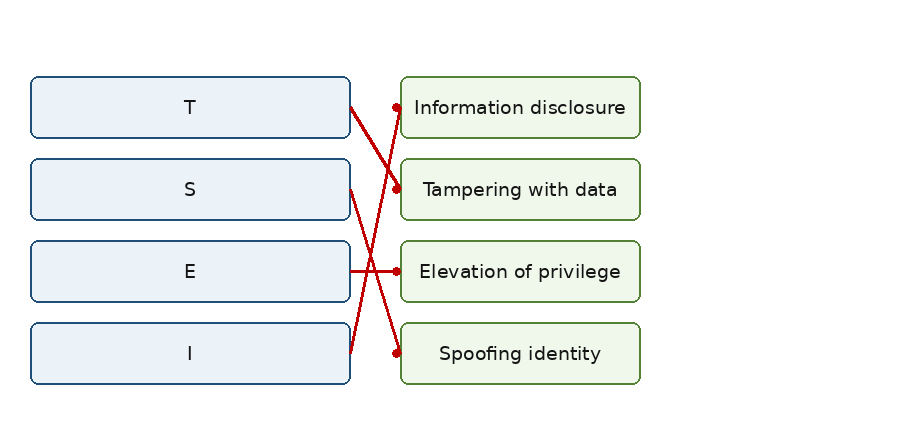
DRAG DROP
Match each STRIDE letter with its threat.
Items to match: S, T, I, E.

Answer is in the explanation below.
CORRECT TEXT
Attacker-focused negative requirements are ______ cases.
Answer is in the explanation below.
Which two prevent injection flaws? (Choose two.)
Select all that apply, then click Submit answer.
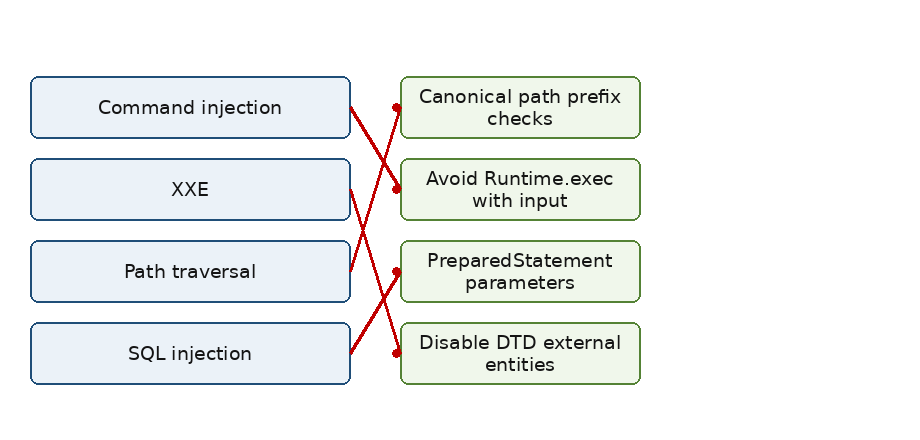
DRAG DROP
Match each flaw with its primary Java defense.
Items to match: SQL injection, XXE, Command injection, Path traversal.

Answer is in the explanation below.