What does the MITRE ATT&CK framework primarily catalog?
Select an option, then click Submit answer.
- ○ Adversary tactics, techniques, and procedures
- ○ Malware file hash blocklists
- ○ Cloud service pricing tiers
- ○ Network device configuration standards
Loading demo links...
Showing 1–12 of 12 questions
What does the MITRE ATT&CK framework primarily catalog?
Select an option, then click Submit answer.
In the cyber kill chain, what follows reconnaissance?
Select an option, then click Submit answer.
Which ATT&CK tactic covers an adversary establishing C2 channels?
Select an option, then click Submit answer.
A hunter maps 'rundll32 executing a malicious DLL' to which tactic phase first?
Select an option, then click Submit answer.
What is a 'technique' in ATT&CK terms?
Select an option, then click Submit answer.
Why do hunters communicate findings with ATT&CK mappings?
Select an option, then click Submit answer.
Which TWO are ATT&CK Enterprise tactics? (Choose two.)
Select all that apply, then click Submit answer.
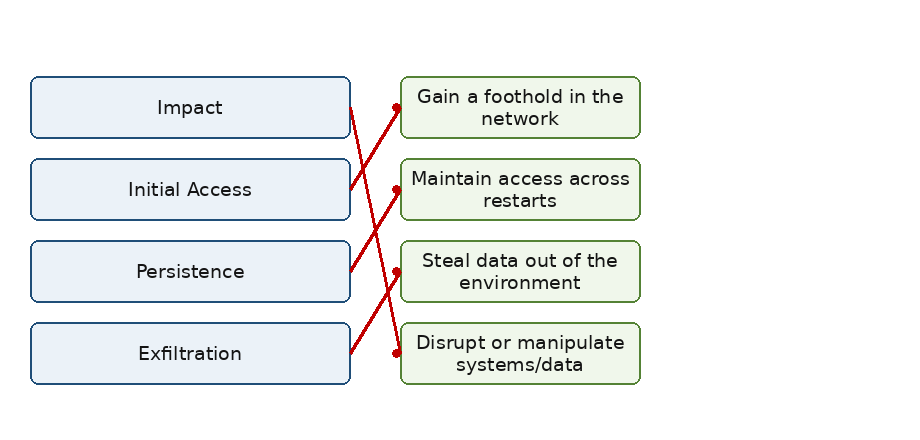
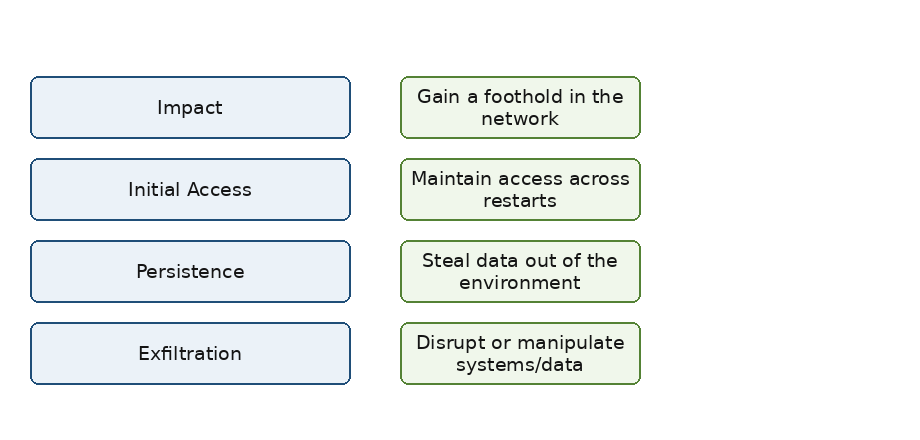
DRAG DROP
Match each tactic to its adversary goal.
Items to match: Initial Access, Persistence, Exfiltration, Impact.

Answer is in the explanation below.
CORRECT TEXT
The ATT&CK catalog of adversary behaviors is maintained by ______.
Answer is in the explanation below.
Which TWO are signs a detection reflects real adversary activity? (Choose two.)
Select all that apply, then click Submit answer.
Which TWO views support detection analysis in Falcon? (Choose two.)
Select all that apply, then click Submit answer.
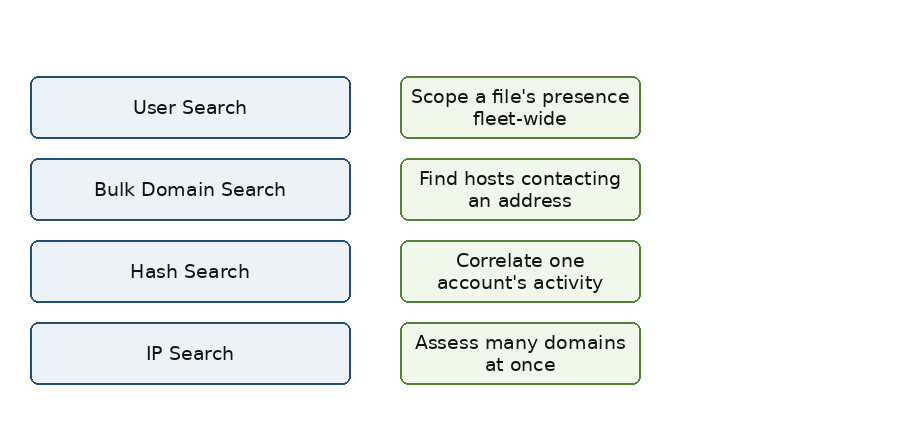
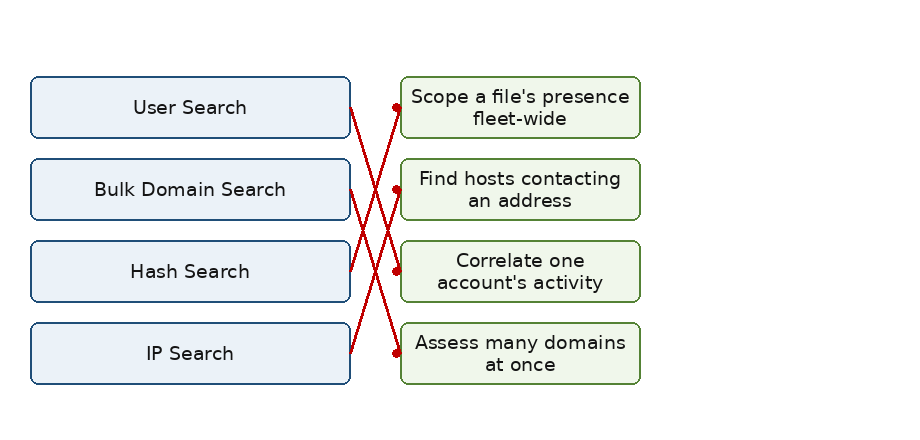
DRAG DROP
Match each search tool to its investigative use.
Items to match: Hash Search, IP Search, User Search, Bulk Domain Search.

Answer is in the explanation below.