What must exist before penetration testing begins on a client system?
Select an option, then click Submit answer.
- ○ Written authorisation from owner
- ○ Verbal agreement with user
- ○ Email from any employee
- ○ Tester judgement of fairness
Loading demo links...
Showing 1–12 of 12 questions
What must exist before penetration testing begins on a client system?
Select an option, then click Submit answer.
During scoping, which constraint most directly affects the depth of an application test?
Select an option, then click Submit answer.
Which two elements belong in a penetration test report finding? (Choose two.)
Select all that apply, then click Submit answer.
CVSS scoring in a report is primarily used to do what?
Select an option, then click Submit answer.
Why are daily checkpoints agreed at the start of an engagement?
Select an option, then click Submit answer.
CORRECT TEXT
The rules defining permitted targets, timing and techniques for a test are its rules of ______.
Answer is in the explanation below.
DRAG DROP
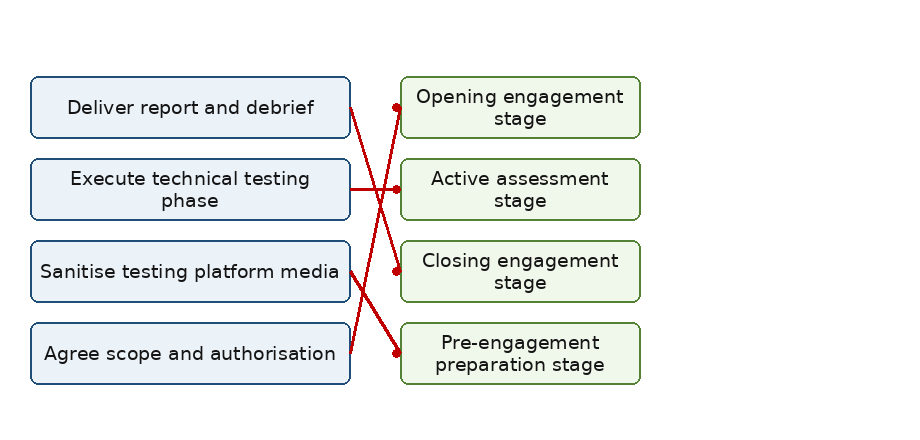
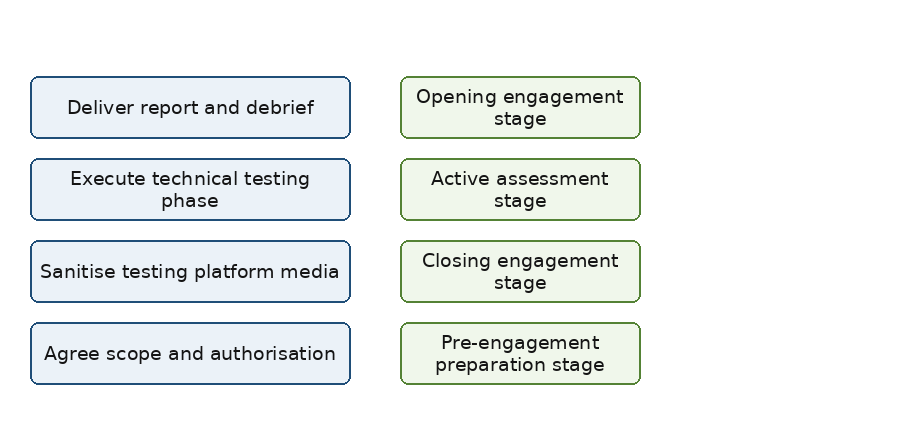
Match each engagement activity to its lifecycle stage.
Items to match: Agree scope and authorisation, Execute technical testing phase, Deliver report and debrief, Sanitise testing platform media.

Answer is in the explanation below.
Which two practices protect client data gathered during testing? (Choose two.)
Select all that apply, then click Submit answer.
A test risks causing denial of service on a fragile legacy system. The tester should do what?
Select an option, then click Submit answer.
Report quality assurance review primarily checks what before delivery?
Select an option, then click Submit answer.
Which two are valid uses of cryptography in engagements? (Choose two.)
Select all that apply, then click Submit answer.
DRAG DROP
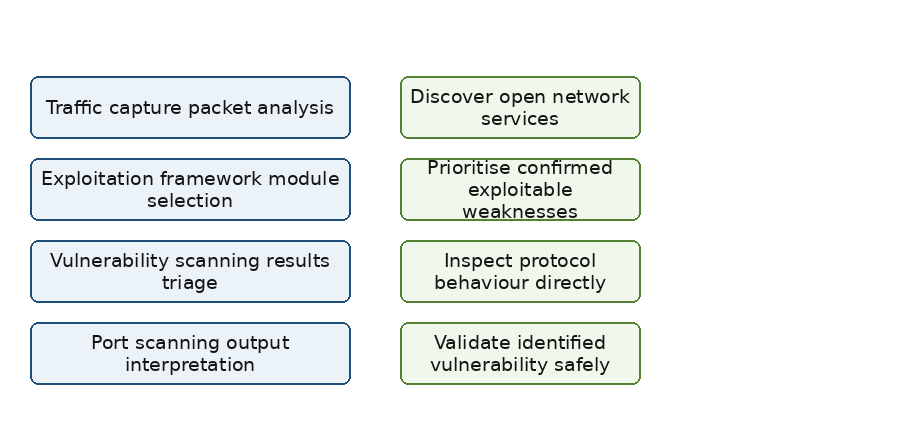
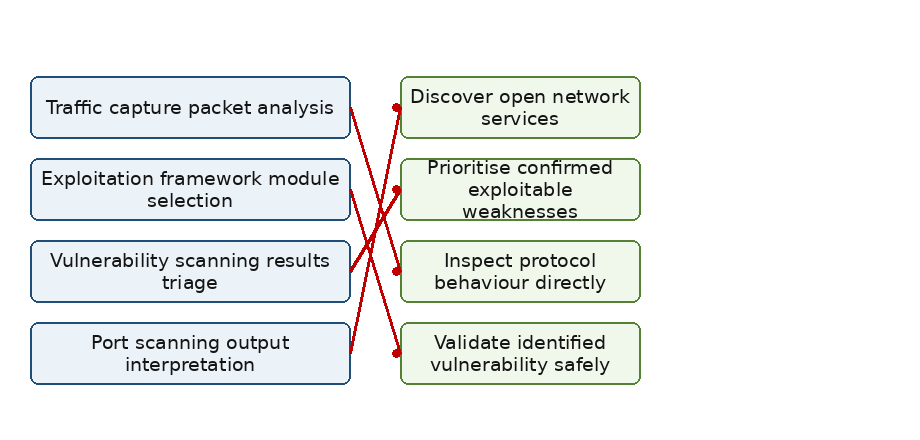
Match each tool purpose to its assessment use.
Items to match: Port scanning output interpretation, Vulnerability scanning results triage, Traffic capture packet analysis, Exploitation framework module selection.

Answer is in the explanation below.