DRAG DROP
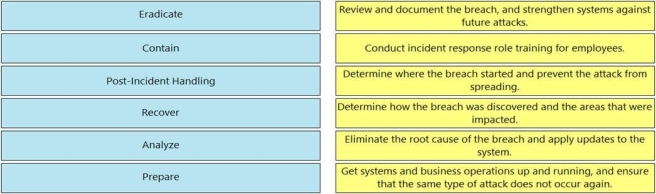
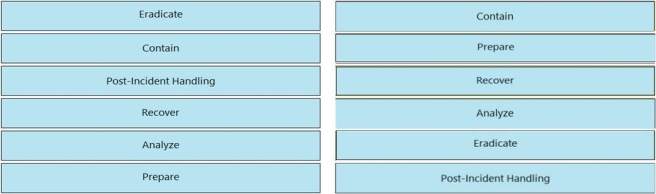
Drag and drop the NIST incident response process steps from the left onto the actions that occur in the steps on the right.
Select and Place:

Answer is in the explanation below.
Loading demo links...
Showing 1–10 of 10 questions
DRAG DROP
Drag and drop the NIST incident response process steps from the left onto the actions that occur in the steps on the right.
Select and Place:

Answer is in the explanation below.
DRAG DROP
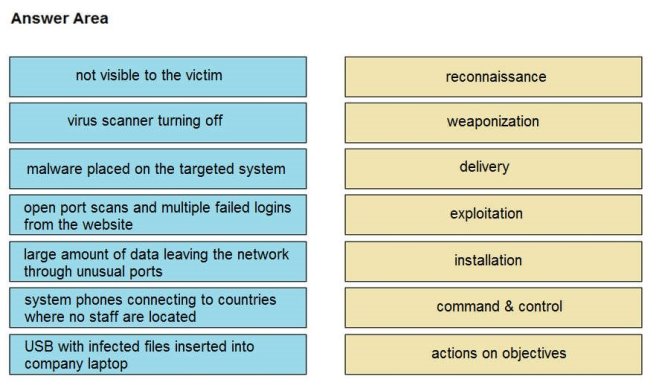
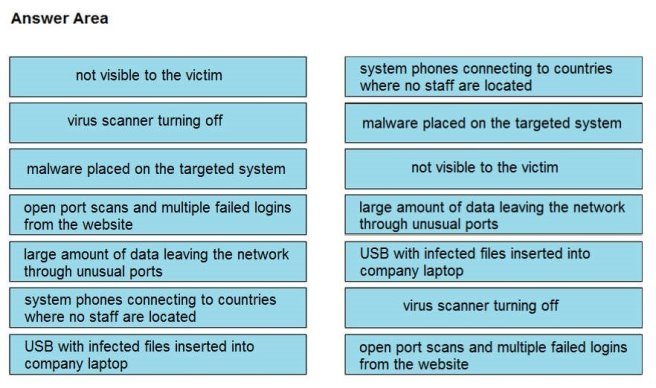
Drag and drop the type of attacks from the left onto the cyber kill chain stages at which the attacks are seen on the right.
Select and Place:

Answer is in the explanation below.
A new malware variant is discovered hidden in pirated software that is distributed on the Internet. Executives have asked for an organizational risk assessment. The security officer is given a list of all assets. According to NIST, which two elements are missing to calculate the risk assessment? (Choose two.)
Select all that apply, then click Submit answer.
incident response playbooks
asset vulnerability assessment
report of staff members with asset relations
key assets and executives
malware analysis report
An organization suffered a security breach in which the attacker exploited a Netlogon Remote Protocol vulnerability for further privilege escalation. Which two actions should the incident response team take to prevent this type of attack from reoccurring? (Choose two.)
Select all that apply, then click Submit answer.
Implement a patch management process.
Scan the company server files for known viruses.
Apply existing patches to the company servers.
Automate antivirus scans of the company servers.
Define roles and responsibilities in the incident response playbook.
Engineers are working to document, list, and discover all used applications within an organization. During the regular assessment of applications from the HR backup server, an engineer discovered an unknown application. The analysis showed that the application is communicating with external addresses on a non-secure, unencrypted channel. Information gathering revealed that the unknown application does not have an owner and is not being used by a business unit. What are the next two steps the engineers should take in this investigation? (Choose two.)
Select all that apply, then click Submit answer.
Determine the type of data stored on the affected asset, document the access logs, and engage the incident response team.
Identify who installed the application by reviewing the logs and gather a user access log from the HR department.
Verify user credentials on the affected asset, modify passwords, and confirm available patches and updates are installed.
Initiate a triage meeting with department leads to determine if the application is owned internally or used by any business unit and document the asset owner.
Employees receive an email from an executive within the organization that summarizes a recent security breach and requests that employees verify their credentials through a provided link. Several employees report the email as suspicious, and a security analyst is investigating the reports. Which two steps should the analyst take to begin this investigation? (Choose two.)
Select all that apply, then click Submit answer.
Evaluate the intrusion detection system alerts to determine the threat source and attack surface.
Communicate with employees to determine who opened the link and isolate the affected assets.
Examine the firewall and HIPS configuration to identify the exploited vulnerabilities and apply recommended mitigation.
Review the mail server and proxy logs to identify the impact of a potential breach.
Check the email header to identify the sender and analyze the link in an isolated environment.
A SOC engineer discovers that the organization had three DDOS attacks overnight. Four servers are reported offline, even though the hardware seems to be working as expected. One of the offline servers is affecting the pay system reporting times. Three employees, including executive management, have reported ransomware on their laptops. Which steps help the engineer understand a comprehensive overview of the incident?
Select an option, then click Submit answer.
Run and evaluate a full packet capture on the workloads, review SIEM logs, and define a root cause.
Run and evaluate a full packet capture on the workloads, review SIEM logs, and plan mitigation steps.
Check SOAR to learn what the security systems are reporting about the overnight events, research the attacks, and plan mitigation step.
Check SOAR to know what the security systems are reporting about the overnight events, review the threat vectors, and define a root cause.
A security analyst receives an escalation regarding an unidentified connection on the Accounting A1 server within a monitored zone. The analyst pulls the logs and discovers that a Powershell process and a WMI tool process were started on the server after the connection was established and that a PE format file was created in the system directory. What is the next step the analyst should take?
Select an option, then click Submit answer.
Isolate the server and perform forensic analysis of the file to determine the type and vector of a possible attack
Identify the server owner through the CMDB and contact the owner to determine if these were planned and identifiable activities
Review the server backup and identify server content and data criticality to assess the intrusion risk
Perform behavioral analysis of the processes on an isolated workstation and perform cleaning procedures if the file is malicious
Which command does an engineer use to set read/write/execute access on a folder for everyone who reaches the resource?
Select an option, then click Submit answer.
chmod 666
chmod 774
chmod 775
chmod 777
An API developer is improving an application code to prevent DDoS attacks. The solution needs to accommodate instances of a large number of API requests coming for legitimate purposes from trustworthy services. Which solution should be implemented?
Select an option, then click Submit answer.
Restrict the number of requests based on a calculation of daily averages. If the limit is exceeded, temporarily block access from the IP address and return a 402 HTTP error code.
Implement REST API Security Essentials solution to automatically mitigate limit exhaustion. If the limit is exceeded, temporarily block access from the service and return a 409 HTTP error code.
Increase a limit of replies in a given interval for each API. If the limit is exceeded, block access from the API key permanently and return a 450 HTTP error code.
Apply a limit to the number of requests in a given time interval for each API. If the rate is exceeded, block access from the API key temporarily and return a 429 HTTP error code.
This free practice test covers the Performing CyberOps Using Core Security Technologies (CBRCOR) (350-201) exam from Cisco. You will find 10 free questions, drawn from the full Study4Pass practice set of 139 questions for this exam. The free sample includes 4 single-answer, 4 multiple-answer and 2 drag-and-drop questions — the same mix of formats you will meet in the full set. The questions follow the same topic balance as the real exam: Such as network design principles, Network technologies, Network security and Network management. The Cisco 350-201 exam is a certification exam that tests a candidate's knowledge and skills related to the Cisco Certified Design Expert (CCDE) program.
The target audience for the Cisco 350-201 exam is individuals who are interested in pursuing a career in network engineering, such as network administrators, network engineers, and network consultants. The Cisco 350-201 exam does not have any prerequisites.
Use the sample the way you would use the real thing: answer each question on your own first, then open the explanation and make sure you understand why the right answer is right. That habit — reasoning instead of memorizing — is what carries over to exam day. When a topic keeps tripping you up, that is your study plan telling you where to go next.
When you finish the sample, do not just count the score — read it. Every missed question names a topic, and the full set lets you train that topic on its own until it stops costing you marks. That loop of test, review and targeted practice is how this set is designed to be used, from the first free question to the last simulation.
Inside the full 350-201 practice set:
Pick an answer for each question and check it straight away — the correct answer and a full explanation appear under the question. There is no time limit and nothing to sign up for. When an explanation is not enough, use Ask AI: this is an AI-Enabled practice test, and Ask AI explains the concept behind the question in plain language. Ready for more? The full 139-question set adds a timed Exam Simulation mode, topic training for your weak areas, and a flagged-question review, so you can practise the way the real exam feels.
Yes — the 10 questions on this page are completely free, with no signup and no payment details needed.
139 questions. The 10 free questions above are a sample of that full set, in the same style and topic balance.
Yes — every question shows the correct answer with an explanation, and Ask AI can explain the concept behind a question in plain words if you want to go deeper.
No. This is a practice test: the questions are written to mirror the real 350-201 exam’s topics and difficulty, not copied from it.