What is threat hunting, fundamentally?
Select an option, then click Submit answer.
- ○ Proactive, hypothesis-driven search for undetected threats
- ○ Reactive alert triage only
- ○ Automated patching of hosts
- ○ Quarterly vulnerability scanning
Loading demo links...
Showing 1–12 of 12 questions
What is threat hunting, fundamentally?
Select an option, then click Submit answer.
What does the Pyramid of Pain rank?
Select an option, then click Submit answer.
Which indicator sits at the Pyramid of Pain apex?
Select an option, then click Submit answer.
What characterizes the highest level of the Threat Hunting Maturity Model?
Select an option, then click Submit answer.
Why do detection tools have inherent limits against new malware?
Select an option, then click Submit answer.
What is a limitation of AI/ML in the SOC?
Select an option, then click Submit answer.
Which two sit low on the Pyramid of Pain (easy for attackers to change)? (Choose two.)
Select all that apply, then click Submit answer.
Which two are automation trade-offs in a SOC? (Choose two.)
Select all that apply, then click Submit answer.
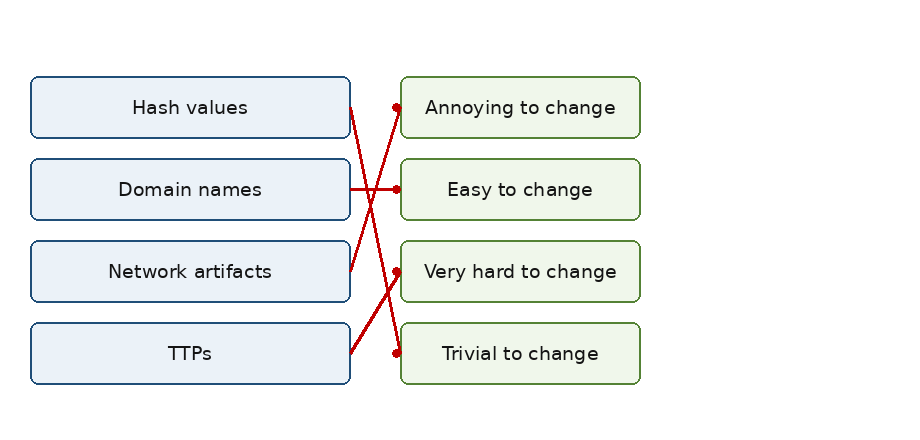
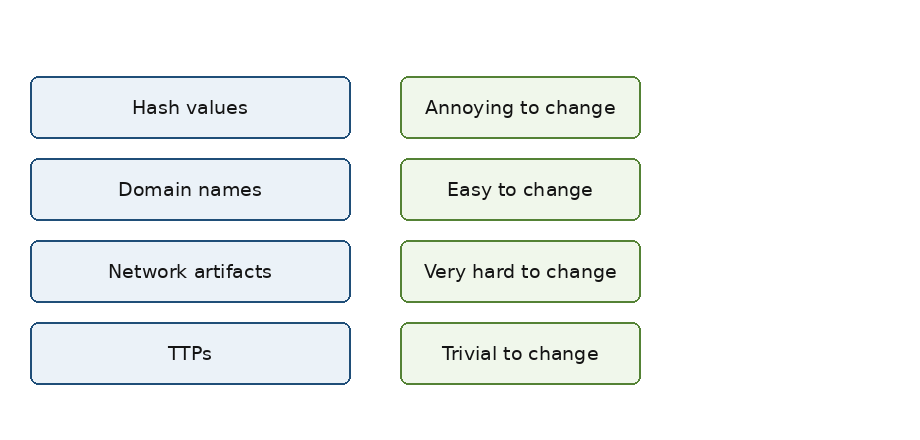
DRAG DROP
Match each Pyramid level with its difficulty for adversaries.
Items to match: Hash values, Domain names, Network artifacts, TTPs.

Answer is in the explanation below.
CORRECT TEXT
Proactive adversary searching is threat ______.
Answer is in the explanation below.
Which two are uses of the Cyber Kill Chain? (Choose two.)
Select all that apply, then click Submit answer.
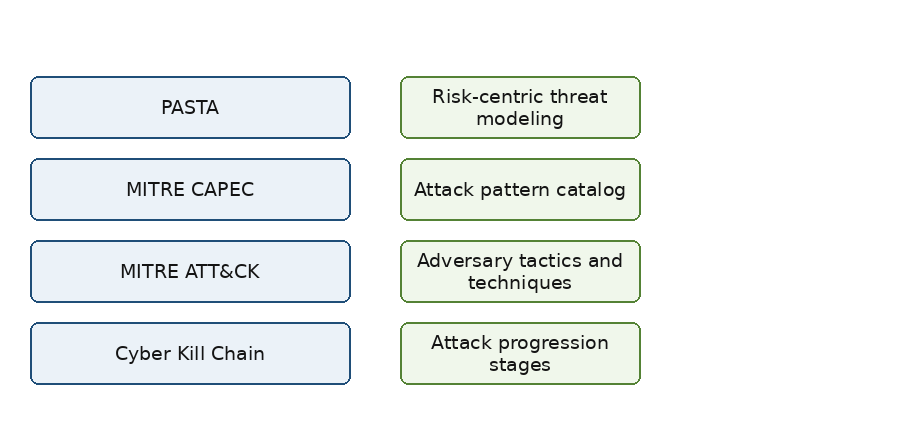
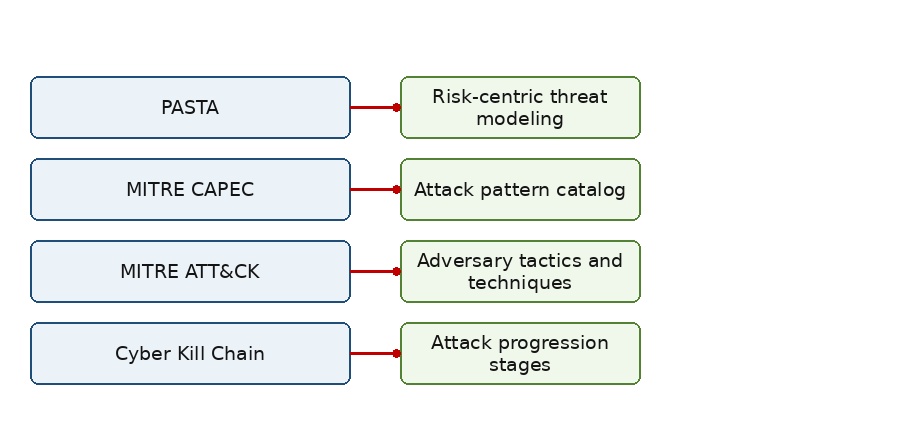
DRAG DROP
Match each framework with its focus.
Items to match: MITRE ATT&CK, Cyber Kill Chain, MITRE CAPEC, PASTA.

Answer is in the explanation below.