Question 1
DRAG DROP
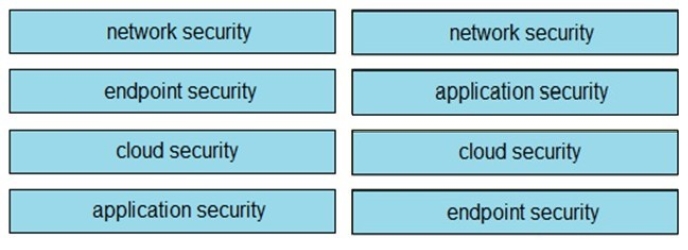
Drag and drop the capabilities on the left onto the Cisco security solutions on the right.
Select and Place:
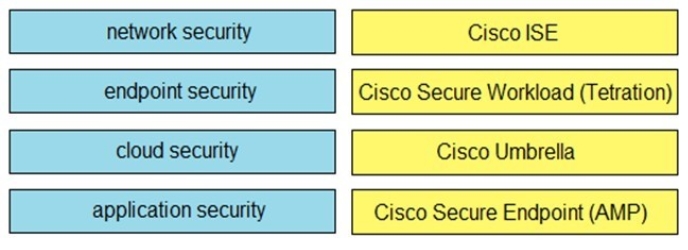
Answer is in the explanation below.
Loading demo links...
Showing 1–10 of 10 questions
DRAG DROP
Drag and drop the capabilities on the left onto the Cisco security solutions on the right.
Select and Place:
Answer is in the explanation below.
An engineer is investigating a ticket from the accounting department in which a user discovered an unexpected application on their workstation. Several alerts are seen from the intrusion detection system of unknown outgoing internet traffic from this workstation. The engineer also notices a degraded processing capability, which complicates the analysis process. Which two actions should the engineer take? (Choose two.)
Select all that apply, then click Submit answer.
Restore to a system recovery point.
Replace the faulty CPU.
Disconnect from the network.
Format the workstation drives.
Take an image of the workstation.
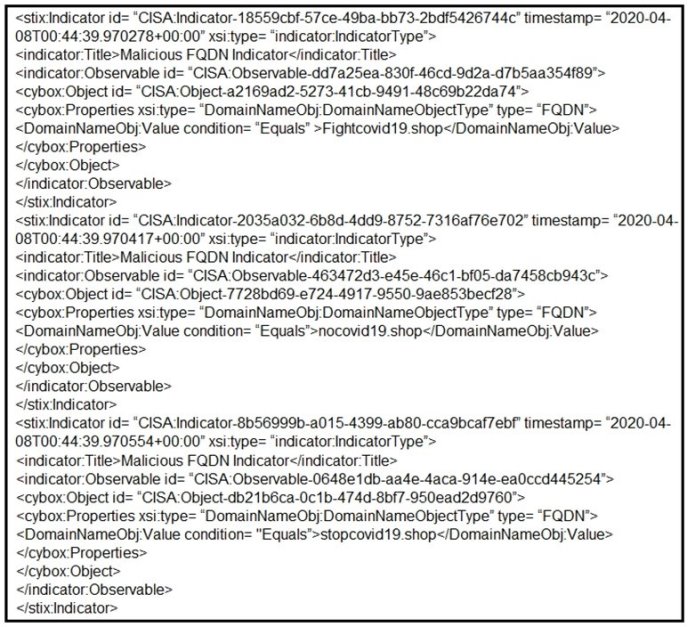
Refer to the exhibit. Which two actions should be taken based on the intelligence information? (Choose two.)
Select all that apply, then click Submit answer.
Block network access to all .shop domains
Add a SIEM rule to alert on connections to identified domains.
Use the DNS server to block hole all .shop requests.
Block network access to identified domains.
Route traffic from identified domains to block hole.
An incident response team is recommending changes after analyzing a recent compromise in which:
 a large number of events and logs were involved;
team members were not able to identify the anomalous behavior and escalate it in a timely manner; several network systems were affected as a result of the latency in detection;
security engineers were able to mitigate the threat and bring systems back to a stable state; and the issue reoccurred shortly after and systems became unstable again because the correct information was not gathered during the initial identification phase.
Which two recommendations should be made for improving the incident response process? (Choose two.)
Select all that apply, then click Submit answer.
Formalize reporting requirements and responsibilities to update management and internal stakeholders throughout the incident-handling process effectively.
Improve the mitigation phase to ensure causes can be quickly identified, and systems returned to a functioning state.
Implement an automated operation to pull systems events/logs and bring them into an organizational context.
Allocate additional resources for the containment phase to stabilize systems in a timely manner and reduce an attack’s breadth.
Modify the incident handling playbook and checklist to ensure alignment and agreement on roles, responsibilities, and steps before an incident occurs.
A security team received reports of users receiving emails linked to external or unknown URLs that are non-returnable and non-deliverable. The ISP also reported a 500% increase in the amount of ingress and egress email traffic received. After detecting the problem, the security team moves to the recovery phase in their incident response plan. Which two actions should be taken in the recovery phase of this incident? (Choose two.)
Select all that apply, then click Submit answer.
verify the breadth of the attack
collect logs
request packet capture
remove vulnerabilities
scan hosts with updated signatures
An organization uses a Windows 7 workstation for access tracking in one of their physical data centers on which a guard documents entrance/exit activities of all personnel. A server shut down unexpectedly in this data center, and a security specialist is analyzing the case. Initial checks show that the previous two days of entrance/exit logs are missing, and the guard is confident that the logs were entered on the workstation. Where should the security specialist look next to continue investigating this case?
Select an option, then click Submit answer.
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\WindowsNT\CurrentVersion\Winlogon
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\WindowsNT\CurrentVersion\ProfileList
HKEY_CURRENT_USER\Software\Classes\Winlog
HKEY_LOCAL_MACHINES\SOFTWARE\Microsoft\WindowsNT\CurrentUser
What is the steganography anti-forensics technique?
Select an option, then click Submit answer.
hiding a section of a malicious file in unused areas of a file
changing the file header of a malicious file to another file type
sending malicious files over a public network by encapsulation
concealing malicious files in ordinary or unsuspecting places

Refer to the exhibit. What should be determined from this Apache log?
Select an option, then click Submit answer.
A module named mod_ssl is needed to make SSL connections.
The private key does not match with the SSL certificate.
The certificate file has been maliciously modified
The SSL traffic setup is improper

Refer to the exhibit. What do these artifacts indicate?
Select an option, then click Submit answer.
An executable file is requesting an application download.
A malicious file is redirecting users to different domains.
The MD5 of a file is identified as a virus and is being blocked.
A forged DNS request is forwarding users to malicious websites.
An engineer received a report of a suspicious email from an employee. The employee had already opened the attachment, which was an empty Word document. The engineer cannot identify any clear signs of compromise but while reviewing running processes, observes that PowerShell.exe was spawned by cmd.exe with a grandparent winword.exe process. What is the recommended action the engineer should take?
Select an option, then click Submit answer.
Upload the file signature to threat intelligence tools to determine if the file is malicious.
Monitor processes as this a standard behavior of Word macro embedded documents.
Contain the threat for further analysis as this is an indication of suspicious activity.
Investigate the sender of the email and communicate with the employee to determine the motives.
This page holds a free practice test for the Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR) (300-215) certification from Cisco. You will find 10 free questions, drawn from the full Study4Pass practice set of 60 questions for this exam. The free sample includes 5 single-answer, 4 multiple-answer and 1 drag-and-drop questions — the same mix of formats you will meet in the full set. The questions follow the same topic balance as the real exam: Cisco Secure Access Architecture, Cisco Secure Access Policies, Cisco Secure Access Deployment and Cisco Secure Access Troubleshooting. The Cisco 300-215 exam is a 90-minute exam associated with the CCNP Security certification.
The target audience for the Cisco 300-215 exam consists of network professionals who have experience configuring and troubleshooting Cisco routers and switches. The Prerequisite for the Cisco 300-215 Exam is a valid Cisco Certified Network Associate (CCNA) certification.
Use the sample the way you would use the real thing: answer each question on your own first, then open the explanation and make sure you understand why the right answer is right. That habit — reasoning instead of memorizing — is what carries over to exam day. When a topic keeps tripping you up, that is your study plan telling you where to go next.
When you finish the sample, do not just count the score — read it. Every missed question names a topic, and the full set lets you train that topic on its own until it stops costing you marks. That loop of test, review and targeted practice is how this set is designed to be used, from the first free question to the last simulation.
Inside the full 300-215 practice set:
Pick an answer for each question and check it straight away — the correct answer and a full explanation appear under the question. There is no time limit and nothing to sign up for. When an explanation is not enough, use Ask AI: this is an AI-Enabled practice test, and Ask AI explains the concept behind the question in plain language. Ready for more? The full 60-question set adds a timed Exam Simulation mode, topic training for your weak areas, and a flagged-question review, so you can practise the way the real exam feels.
Yes — the 10 questions on this page are completely free, with no signup and no payment details needed.
60 questions. The 10 free questions above are a sample of that full set, in the same style and topic balance.
Yes — every question shows the correct answer with an explanation, and Ask AI can explain the concept behind a question in plain words if you want to go deeper.
No. This is a practice test: the questions are written to mirror the real 300-215 exam’s topics and difficulty, not copied from it.