Free SC-200 – Microsoft Security Operations Analyst Practice Test Question

Free demo downloads

Loading demo links...

Showing 7–9 of 15 questions

Question 7 (Mixed Questions)

You provision Azure Sentinel for a new Azure subscription.

You are configuring the Security Events connector.

While creating a new rule from a template in the connector, you decide to generate a new alert for every event.

You create the following rule query.
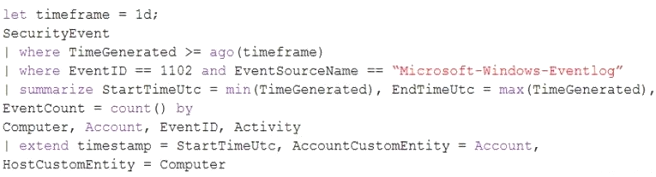
By which two components can you group alerts into incidents? Each correct answer presents a complete solution.

NOTE: Each correct selection is worth one point.

Select all that apply, then click Submit answer.

  • ○

    user

  • ○

    resource group

  • ○

    IP address

  • ○

    computer

Question 8 (Mixed Questions)

You are configuring Azure Sentinel.

You need to send a Microsoft Teams message to a channel whenever a sign-in from a suspicious IP address is detected.

Which two actions should you perform in Azure Sentinel? Each correct answer presents part of the solution.

NOTE: Each correct selection is worth one point.

Select all that apply, then click Submit answer.

  • ○

    Add a playbook.

  • ○

    Associate a playbook to an incident.

  • ○

    Enable Entity behavior analytics.

  • ○

    Create a workbook.

  • ○

    Enable the Fusion rule.

Question 9 (Mixed Questions)

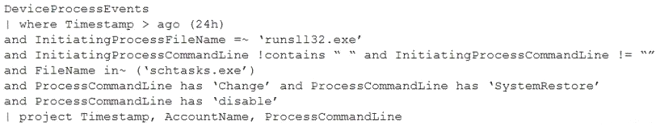
You have the following advanced hunting query in Microsoft 365 Defender.

You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.

Which two actions should you perform? Each correct answer presents part of the solution.

NOTE: Each correct selection is worth one point.

Select all that apply, then click Submit answer.

  • ○

    Create a detection rule.

  • ○

    Create a suppression rule.

  • ○

    Add | order by Timestamp to the query.

  • ○

    Replace DeviceProcessEvents with DeviceNetworkEvents.

  • ○

    Add DeviceId and ReportId to the output of the query.